FBI Tells Its Employees to Assume Hackers Have Their Personal Data
In a recent internal memo, the FBI has advised its employees to operate under the assumption that hackers may have accessed their personal information. This warning follows claims by the hacking group ShinyHunters, which alleges that it successfully breached the bureau's jobs site and potentially acquired sensitive details about current and former employees. The memo underscores the seriousness of the situation and the need for employees to remain vigilant regarding their personal security.
The context of this warning stems from the growing trend of cyberattacks targeting government agencies and large organizations. ShinyHunters is known for its data breaches and selling stolen information on the dark web. The FBI's acknowledgment of the threat highlights the vulnerability of even the most secure institutions to cybercriminals. It also raises questions about the effectiveness of the bureau’s cybersecurity measures and its ability to protect sensitive data.
This development is significant for the market, as it reflects the ongoing risk of data breaches within high-profile organizations. Trust in the cybersecurity of governmental institutions is paramount, and incidents like this can have broader implications for public confidence in the security of personal data. Moreover, as more individuals become aware of the potential exposure of their information, there may be increased demand for cybersecurity services and solutions.
Industry reactions have been mixed, with cybersecurity experts emphasizing the importance of robust security protocols and employee training to mitigate risks. Some experts have suggested that the FBI's memo serves as a wake-up call for all organizations to reassess their cybersecurity strategies. As the frequency and sophistication of attacks grow, the need for comprehensive security measures cannot be overstated.
Looking ahead, the FBI will likely intensify its efforts to investigate the breach and identify the extent of the data compromised. Employees may be advised to take additional precautions, such as monitoring their accounts for suspicious activity. This incident could prompt further discussions on improving cybersecurity frameworks within government agencies and beyond.

CoinMagnetic Team
Crypto investors since 2017. We trade with our own money and test every exchange ourselves.
Updated: September 2026
From our insights:
Related news
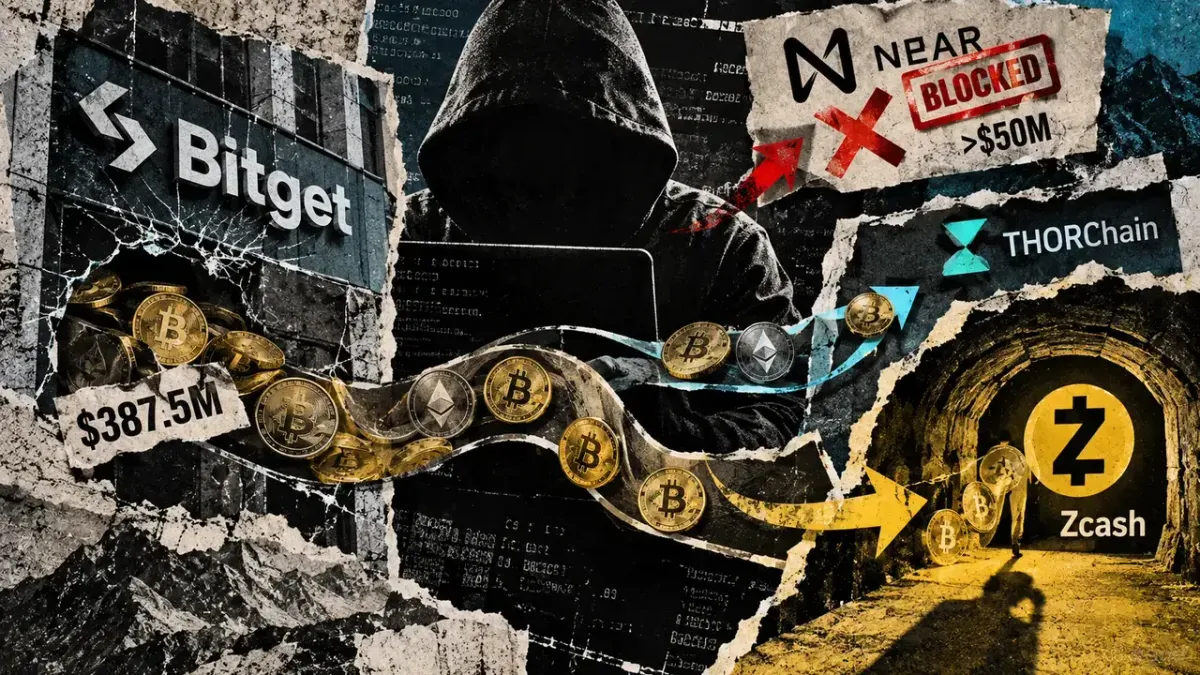
Bitget’s hackers turn to Zcash after $50 million laundering route gets blocked
Bitget hacker moves $3.8 million in ZEC to Zcash's Ironwood pool after swap rejection
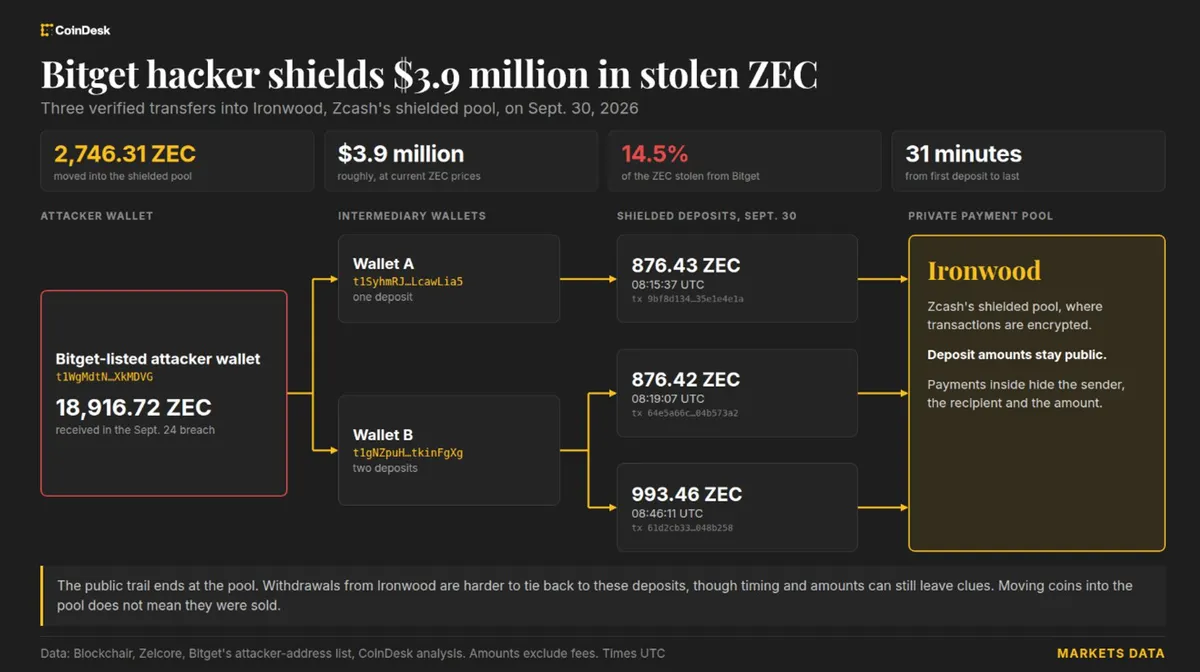
$4 million in stolen Zcash moved to Ironwood, complicating recovery efforts
OpenAI, Google and Meta sign voluntary AI audit pact with no penalties
SlowMist traces Bitget hack activity to Aug. 31 zero-day exploit