Fomopeek app exploits iOS vulnerabilities to steal $580,000 in USDT
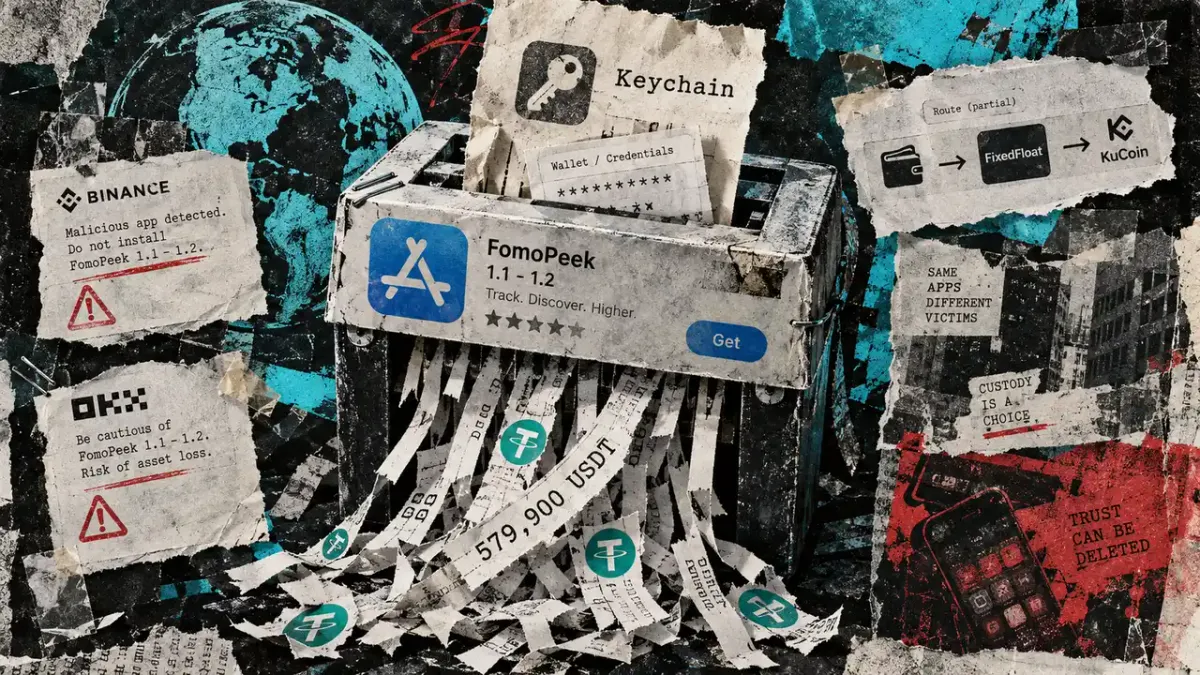
Fomopeek, a malicious iPhone application that made its way onto Apple’s App Store, has been implicated in the theft of nearly $580,000 in USDT. The alarming discovery was made by the blockchain security firm SlowMist, which initiated an investigation after receiving multiple reports from users about stolen assets associated with compromised private keys. The app was reportedly linked to previous versions installed by some victims, specifically versions 1.1 and 1.2, which may have contained vulnerabilities that allowed for this exploitation.
The context surrounding this incident highlights the ongoing challenges faced by app developers and users within the mobile ecosystem, particularly concerning security. Despite Apple's stringent app review processes, malicious applications can still occasionally slip through the cracks. The Fomopeek incident serves as a reminder of the potential risks users face when installing applications, even from trusted sources like the App Store. The nature of the vulnerability exploited by Fomopeek raises questions about the efficacy of existing security measures.
This breach could have significant implications for the cryptocurrency market, particularly for those holding USDT and other assets on mobile wallets. The incident emphasizes the importance of safeguarding private keys and the need for users to remain vigilant against potential threats. As more digital assets are managed via mobile applications, the risk of similar incidents may increase. This situation could lead to a decline in trust among users who rely on mobile wallets for their transactions and holdings.
Industry experts have expressed concern over the implications of this breach, noting that it underscores the necessity for enhanced security protocols both from app developers and device manufacturers. The incident has prompted discussions regarding the development of more robust verification processes for applications that interact with cryptocurrencies. Additionally, it may lead to greater scrutiny from regulatory bodies regarding mobile app security standards in the cryptocurrency sector.
Looking ahead, it will be crucial for Apple and other tech companies to address the vulnerabilities that allowed Fomopeek to operate undetected. Users may need to adopt more stringent security practices, such as using hardware wallets or multi-factor authentication, to protect their assets. The cryptocurrency community will be watching closely to see how this incident influences both app security measures and user behavior in the future.

CoinMagnetic Team
Crypto investors since 2017. We trade with our own money and test every exchange ourselves.
Updated: September 2026
From our insights:
Related news
DeepSeek to address UN Security Council on AI risks alongside Dario Amodei
Lummis blames Democrats for failed crypto Clarity Act vote
Federal approval won’t guarantee success for Agora, Catena, and Bastion
Regulatory clarity on crypto relies on officials, not Congress, says White House
PQLN enhances Bitcoin's quantum safety but raises privacy concerns for Lightning