Indian certificate firm eMudhra exposes Ethereum nodes to forged trust issues
We are closely following a critical security oversight involving Indian digital certificate issuer eMudhra, which recently compromised certain Ethereum validator setups running Teku and Besu clients. The blunder inadvertently permitted these specific node configurations to accept and trust forged certificates, creating a potential vulnerability within the broader network architecture. Fortunately, client developers moved swiftly to deploy emergency patches and updates, aiming to isolate the issue before it could escalate into a wider network disruption. Default Ethereum mainnet nodes remained unexposed to the vulnerability, mitigating the immediate danger to the broader blockchain ecosystem.
To understand the gravity of this event, we have to look at how validator clients interact with external certificate authorities. Ethereum clients like Teku and Besu rely on operating system trust stores or bundled certificates to secure TLS connections for various networking endpoints and remote procedure calls. When a recognized certificate issuer like eMudhra experiences a foundational security lapse, the ripple effects can bypass traditional crypto-native defenses by exploiting trust assumptions at the infrastructure level. This incident highlights the hidden dependencies that blockchain protocols share with traditional public key infrastructure and legacy web security standards.
For the wider digital asset market, this situation serves as a sharp reminder that decentralization extends far beyond consensus mechanisms and token distribution. Infrastructure security depends heavily on the weakest link in the operational chain, whether that is a smart contract, a validator client, or an external certificate authority. While financial losses were avoided in this instance, market participants must recognize that infrastructure-layer vulnerabilities can introduce systemic risk. Institutional investors and node operators are increasingly evaluating not just client code, but the entire software supply chain required to keep validators online and secure.
Industry experts and core developers have been quick to praise the rapid response time of the Teku and Besu teams, noting that swift coordination prevented any widespread exploitation. Security researchers have emphasized that node operators need to audit their underlying operating system dependencies more rigorously rather than focusing solely on execution and consensus client software. Discussions across developer forums are already turning toward hardening client configurations to minimize reliance on third-party certificate authorities wherever possible.
Looking ahead, we expect client developers to implement stricter validation checks and default settings that reduce reliance on external root certificates. The episode will likely prompt a comprehensive review across multiple client implementations to identify similar infrastructure blind spots. As the network continues to mature, securing these peripheral layers will remain a top priority for developers striving to build truly resilient decentralized infrastructure.

CoinMagnetic Team
Crypto investors since 2017. We trade with our own money and test every exchange ourselves.
Updated: October 2026
From our insights:
Related news
Language-model scan uncovers three flaws threatening bitcoin nodes on Windows and Macs
CFTC chair warns autonomous AI agents and smart fridges will challenge financial rules
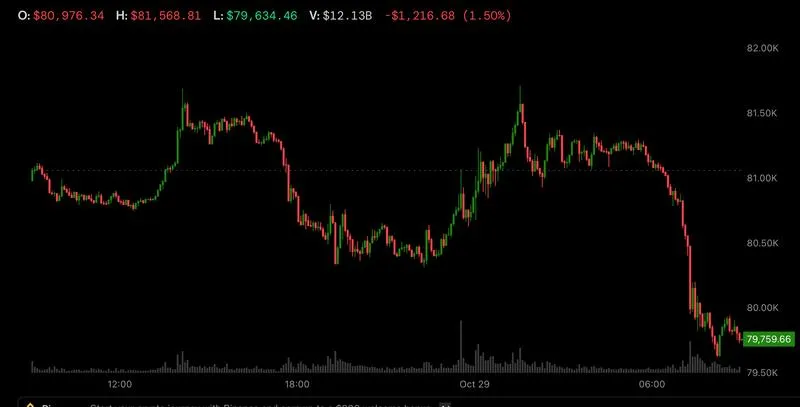
Samsung-led tech jitters and Fed stance drag bitcoin under $80,000
Tampered Ledger wallets cost Singapore users $2.7M: Police
Datavault AI reports locked bitcoin in Biconomy since June as shares drop