NEAR Intents identifies hacker, issues 48-hour ultimatum for $3.8 million theft
NEAR Intents recently made headlines after announcing that it has identified the hacker responsible for a significant breach that compromised $3.8 million from its protocol. Alex Shevchenko, the general manager of NEAR Intents, publicly addressed the hacker, stating, "We have identified you, sir," during an announcement on Friday. The company has now issued a 48-hour ultimatum for the hacker to return the stolen funds, highlighting the urgency and seriousness of the situation.
The hack has raised concerns within the NEAR ecosystem and the broader crypto community. NEAR Intents has been a prominent player in the blockchain space, and this incident poses a potential threat to its reputation and user trust. The breach not only affects the immediate stakeholders but also raises questions about the security protocols in place and the vulnerabilities that allowed such an event to occur.
This incident matters significantly for the market, as it could lead to increased scrutiny over security measures across various protocols. Investors and users might become more cautious when interacting with platforms that have experienced breaches, potentially impacting their overall activity and investment strategies. If the hacker does not comply with the ultimatum, it may set a precedent for how similar situations are handled in the future, influencing market sentiment.
Industry reactions have been varied, with some experts expressing support for NEAR Intents' decisive action while others caution against the effectiveness of public ultimatums. Security professionals have pointed out that while identifying a hacker is a step forward, returning the funds is often more complex. The broader crypto community is watching closely, as this situation could either reinforce trust in NEAR Intents or highlight potential systemic risks within the blockchain space.
Looking ahead, the outcome of this situation will be crucial. If the hacker returns the funds, it could serve as a valuable lesson in accountability and deterrence against future breaches. Conversely, if no resolution is reached, NEAR Intents may need to implement stronger security measures and possibly reevaluate its engagement strategy with users to restore confidence in its platform.

CoinMagnetic Team
Crypto investors since 2017. We trade with our own money and test every exchange ourselves.
Updated: October 2026
From our insights:
Related news
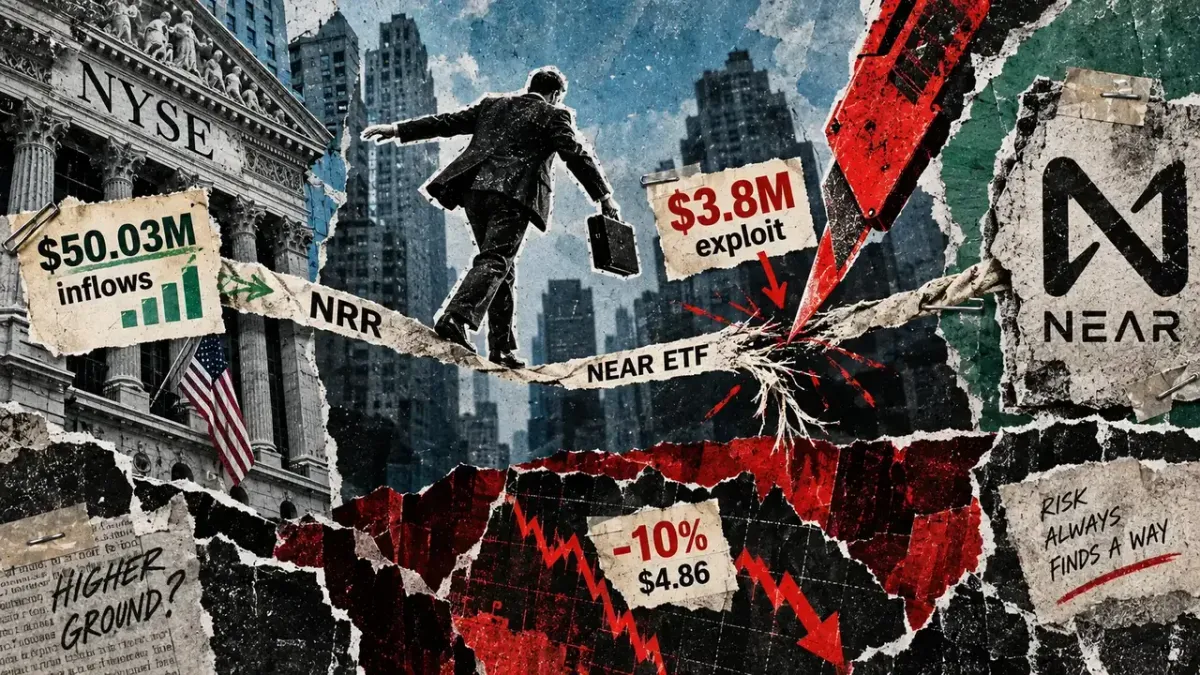
NEAR token drops 10% following $3.8 million exploit as ETF launch coincides
NEAR Intents to compensate users after $3.8M exploit linked to Bitget breach
NEAR Intents hit by $3.8 million exploit as crypto's rough year of hacks continues
Q3 crypto security breaches exceed $1B following Bitget's $388M hack
Crypto hacks resulted in $1.26 billion lost as bitcoin soared in Q3 2026