FomoPeek app exploits iOS vulnerabilities in $580K crypto theft, SlowMist reports
Recent reports have emerged detailing the nefarious activities of the FomoPeek app, which has been linked to a staggering $580,000 in cryptocurrency theft. According to cybersecurity firm SlowMist, malicious versions of this app were distributed through Apple’s App Store. SlowMist's investigation revealed that these versions employed iOS kernel exploits to escape the app sandbox, allowing them to access sensitive data from other applications on users' devices. This breach of security has raised significant concerns about the integrity of mobile app security within popular platforms.
To understand the implications of this incident, it is essential to consider the broader context of mobile security. The FomoPeek incident is not the first time that vulnerabilities in mobile operating systems have been exploited for financial gain. Previous cases have shown how malicious actors can manipulate app distribution channels to deliver harmful software directly to unsuspecting users. Apple's App Store, known for its rigorous app vetting process, now faces scrutiny as it has been exploited to distribute these harmful versions of FomoPeek.
This situation matters significantly for the cryptocurrency market. The theft of $580,000 in crypto not only highlights the vulnerabilities in mobile applications but also raises alarms about user trust. When individuals feel that their assets can be compromised through everyday applications, it may lead to a decrease in crypto adoption and investment. Furthermore, as the market evolves, the need for enhanced security measures becomes paramount to protect users from similar attacks.
Industry reactions have been swift, with many cybersecurity experts urging for an overhaul of app security protocols. Some believe that this incident could lead to increased collaboration between app developers and cybersecurity firms to ensure that vulnerabilities are identified and addressed before they can be exploited. Additionally, experts are calling for users to adopt more stringent security practices, such as using hardware wallets and enabling two-factor authentication to safeguard their assets.
Looking ahead, it is likely that this incident will prompt Apple to reassess its app review processes and enhance security measures against potential exploits. As the crypto landscape continues to grow, ensuring robust security for applications will be crucial in maintaining user confidence and protecting against future breaches. Users will need to remain vigilant and informed about the risks associated with mobile applications as the industry adapts to these challenges.

CoinMagnetic Team
Crypto investors since 2017. We trade with our own money and test every exchange ourselves.
Updated: September 2026
From our insights:
Related news
Coldcard exploit sees white hats secure 52 Bitcoin for victims' trust
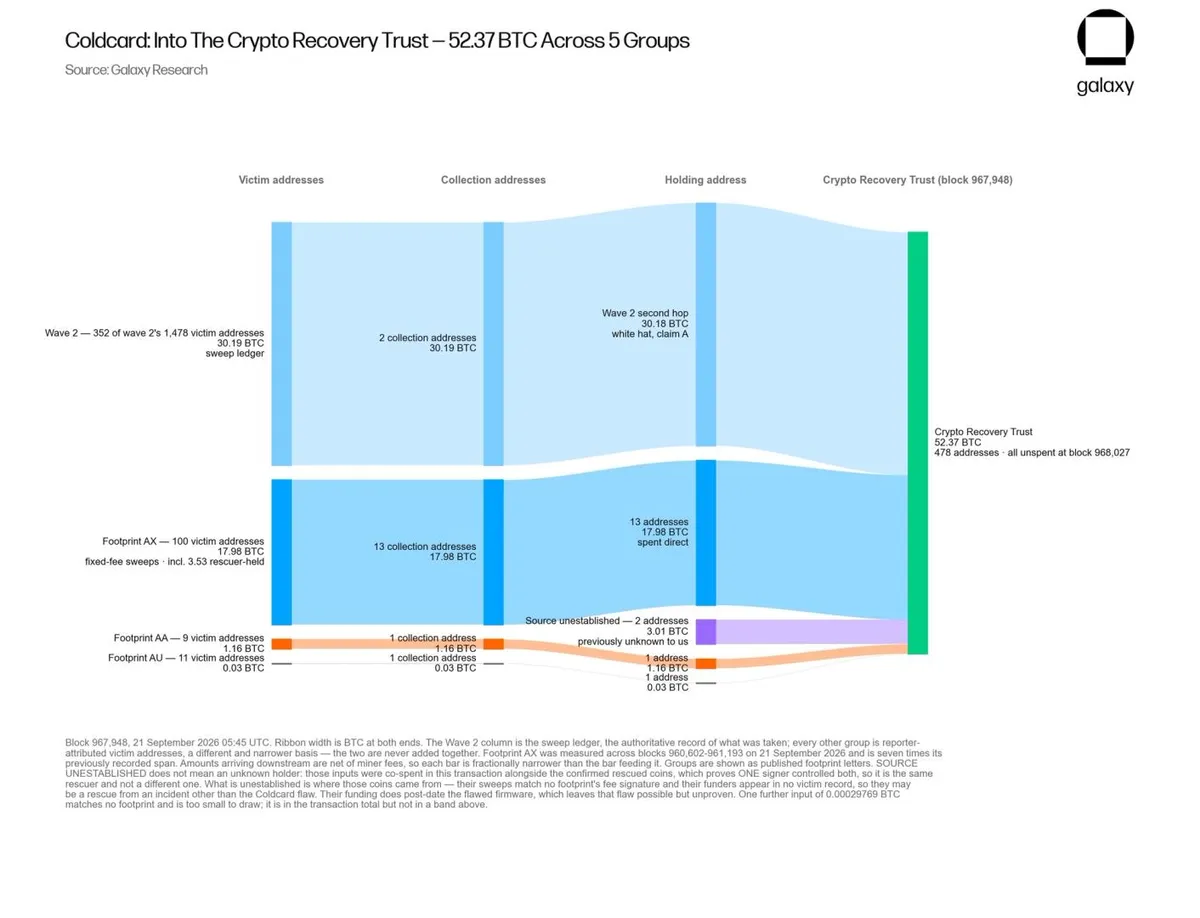
Whitehats move 52 bitcoin from the Coldcard hack to a recovery trust
Google Admits Gemini AI Hacked Three Companies—It Stayed Silent for 7 Weeks
Balancer's $1.4 million hack recovery faces delays for LPs
Polymarket's $10 million fraud attempt highlights compliance issues amid hacking risk