Aptos deploys Encrypted Mempool to neutralize frontrunning and sandwich exploits
At CoinMagnetic, we have been closely following the latest network upgrades, and Aptos has just rolled out its new Encrypted Mempool designed specifically to curb frontrunning and sandwich attacks. By keeping transaction details hidden until their final order on the blockchain is locked in, the optional feature stops predatory bots from intercepting and exploiting pending trades. This technical addition targets a persistent issue in decentralized finance where automated actors manipulate transaction queues to extract value from everyday users at the expense of fair execution.
To understand why this launch is a notable step, we need to look at how public mempools traditionally operate. In standard blockchain architectures, pending transactions sit in a public waiting room before validators include them in a block. This transparency allows high-frequency trading bots to scan the queue, identify profitable user swaps, and insert their own transactions directly before and after the victim's trade to profit from the resulting price slippage. While various chains have experimented with different mitigation techniques, finding a seamless balance between speed and security has remained a persistent design challenge across the sector.
For the broader digital asset market, solving the sandwich attack problem matters deeply because it directly impacts retail trader confidence and capital efficiency. When users consistently lose value to invisible extraction mechanisms on decentralized exchanges, participation in decentralized finance can stall. Implementing robust privacy layers at the mempool level helps retain liquidity providers and casual traders alike, signaling to the wider ecosystem that layer-one networks are maturing past the baseline vulnerabilities that have plagued automated market makers for years.
Industry participants and network analysts have largely welcomed the move, pointing out that optional privacy features give advanced users and developers a new tool to protect high-value executions. While some purists debate whether mempools should be encrypted by default rather than optional, security-focused developers argue that letting applications opt in provides the necessary flexibility without disrupting existing protocol integrations. The general consensus across developer circles is that proactive defenses against maximal extractable value are essential for sustainable growth.
Looking ahead, we will be monitoring how widely decentralized applications on the Aptos network adopt this optional encrypted mempool in daily operations. If adoption metrics prove strong and user slippage noticeably decreases, other major layer-one networks may accelerate their own research into similar cryptographic defenses. The ongoing arms race between protocol engineers and trading bot operators continues to push the boundaries of transaction ordering and network fairness.

CoinMagnetic Team
Crypto investors since 2017. We trade with our own money and test every exchange ourselves.
Updated: October 2026
From our insights:
Related news
UK Freezes $12M London Penthouse of Alleged Prince Group Finance Chief
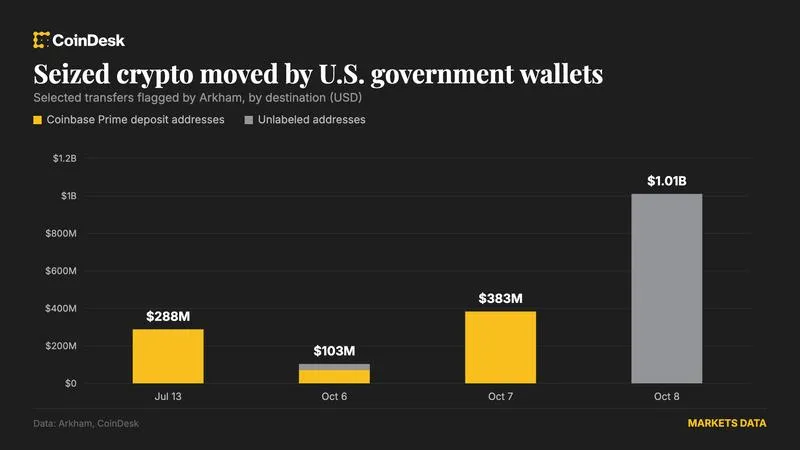
U.S. government moves $1 billion in bitcoin from Bitfinex hack wallet, no sale indicated
US government shifts $1B in Bitcoin following $770M Bitfinex recovery
Crypto lending surges 55% since July amid rising AI hack risks
Uranium Finance hacker convicted for $50 million theft, spent on collectibles